
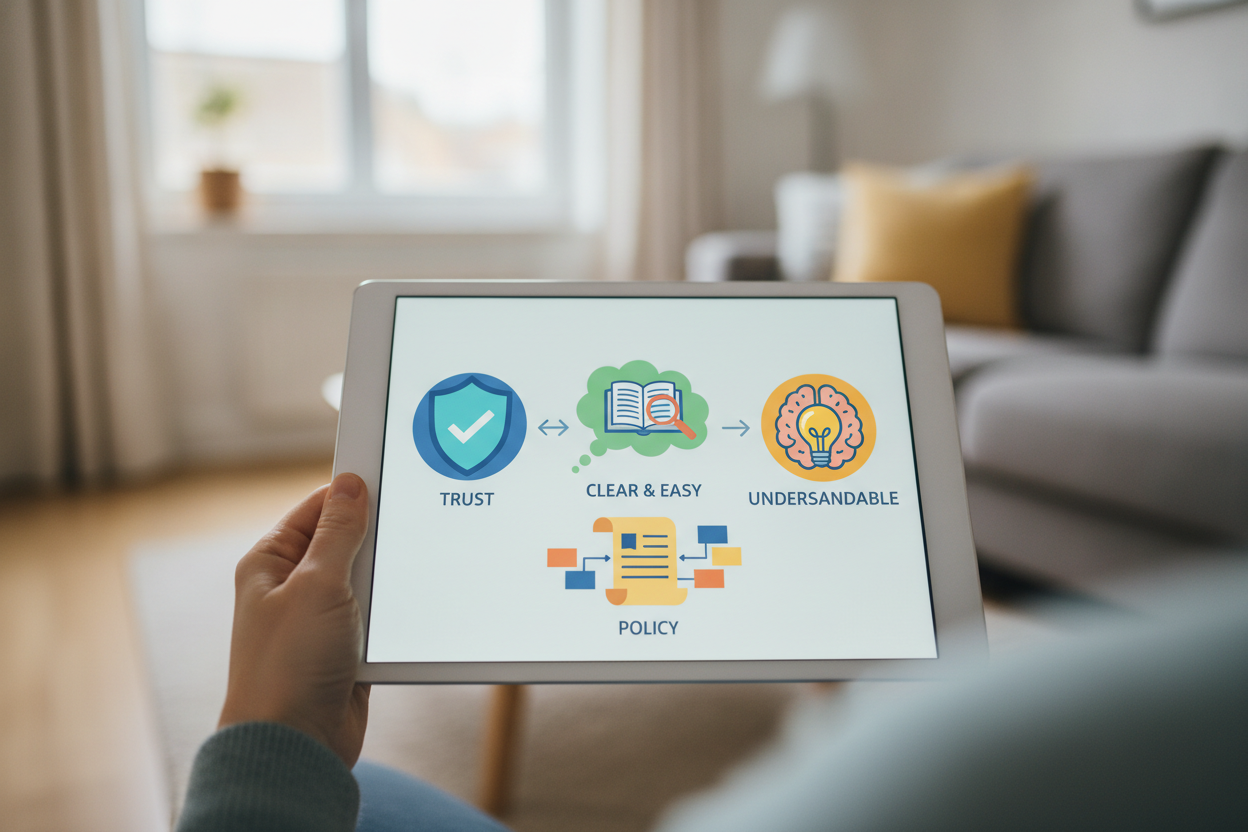
Most people do not read privacy policies because many are difficult to understand. Dense language, vague promises, and long blocks of text make important information easy to miss. Yet a privacy policy should be more than a legal requirement. It is a trust signal that shows users how seriously an organization treats their personal information.
The best policies use plain language and answer the questions people actually have. What data is collected? Why is it collected? Who receives it? How long is it stored? When these answers are visible and direct, users can make informed decisions with more confidence. Clarity is especially important for businesses that operate across regions or collect sensitive information.
Readable policies also support internal alignment. When product, marketing, legal, and support teams all understand the same rules, there is less confusion about what can be shared and how data should be handled. That consistency reduces risk and improves customer communication.
Updating policies regularly matters too. As tools, vendors, and regulations change, the policy must reflect real practices rather than outdated assumptions. A well-written privacy policy is not just a compliance document. It is part of the user experience, and when done well, it helps build long-term trust.
Leave a Reply